Quick answer: to verify that a DNS change has been applied, query the authoritative name server (the one that contains the zone) and then public resolvers (e.g. 8.8.8.8 or 1.1.1.1). The TTL (Time To Live) indicates how long resolvers keep the old value in cache — lowering the TTL before a migration speeds the transition, but remember to raise it again afterwards.
Prerequisites
- Access to your Client Area (if the zone is managed via our interface).
- Access to cPanel if the zone is managed from your hosting account (we show how below).
- A terminal with
dig(Linux/macOS) ornslookup(Windows) to run the checks. You can also use public resolvers (8.8.8.8, 1.1.1.1) to verify propagation. - Before any major change: export or note the current zone (backup the records).
Clear reminder: what is TTL and how does propagation work?
TTL in simple terms
The TTL is the duration (in seconds) during which a DNS response is kept in cache by resolvers (ISPs, public DNS resolvers). Example: TTL = 3600 means that a resolver can reuse the same response for one hour. If you change a record, resolvers that still have the old version cached will continue to use it until the TTL expires.
Propagation ≠ delay in application at the authoritative name server
- The update is first written to the authoritative name server (quickly).
- "Propagation" refers to the period during which resolvers across the Internet expire their cache and begin querying the authoritative name server for the new value.
- Some ISPs or DNS resolvers may not strictly honor the TTL and can retain cached records for longer — you cannot control this behavior.
Check propagation: quick checks (commands and how to interpret them)
Run these checks in order to diagnose where the discrepancy lies between what you intended to apply and what the network sees.
- View the name servers (to determine who is authoritative):
dig +short NS votredomaine.tld
Interpret: if the list does not contain the expected servers (e.g.ns1.capconnect.comns1.capconnect.com), the zone may be managed elsewhere (at the registrar or by a third party). - Query an authoritative server directly:
dig @ns1.capconnect.com votredomaine.tld A +noall +answer
If the authoritative server returns the new value, the change has been published by the zone's manager. - Check propagation from public resolvers:
dig @8.8.8.8 votredomaine.tld A +short
 dig @1.1.1.1 votredomaine.tld A +short
If these resolvers return the old IP, propagation is incomplete in those caches. - Trace the resolution (useful for spotting an incorrect delegation):
dig +trace votredomaine.tld
This output shows the chain from the root; it helps identify if the NS delegation is incorrect. - Read the effective TTL:
In the ANSWER section of dig,
digyou will see a line like:votredomaine.tld. 299 IN A 93.184.216.34
votredomaine.tld. 299 IN A 93.184.216.34299The first number (here 299) is the remaining TTL (in seconds) for this answer.
If you are using Windows (nslookup)
Equivalent command to query a resolver:
nslookup -type=A votredomaine.tld 8.8.8.8nslookup does not always show the TTL as clearly as dig, but it confirms the value returned by a given server.
Verify that the zone has been updated on the authoritative server
- Identify the NS servers as shown above (
dig +short NS) - Query one of the listed servers with
dig @nsX(replacensXwith one of the NS returned). - If the authoritative server returns the old value, the change was not applied correctly — re‑open the zone editor at the provider hosting the zone.
Check and modify the TTL in cPanel (step‑by‑step)
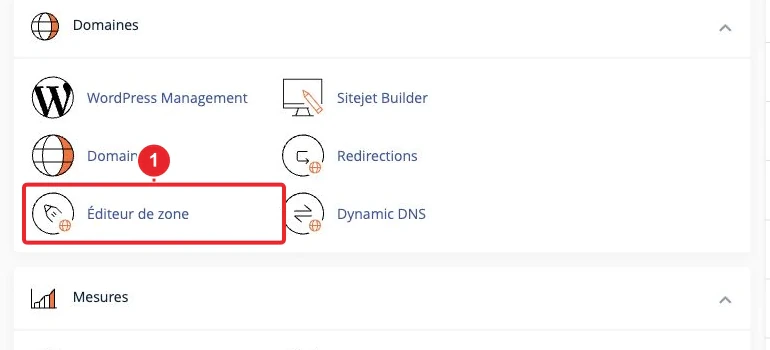
- Log in to cPanel (see How do I access my cPanel account? if necessary).
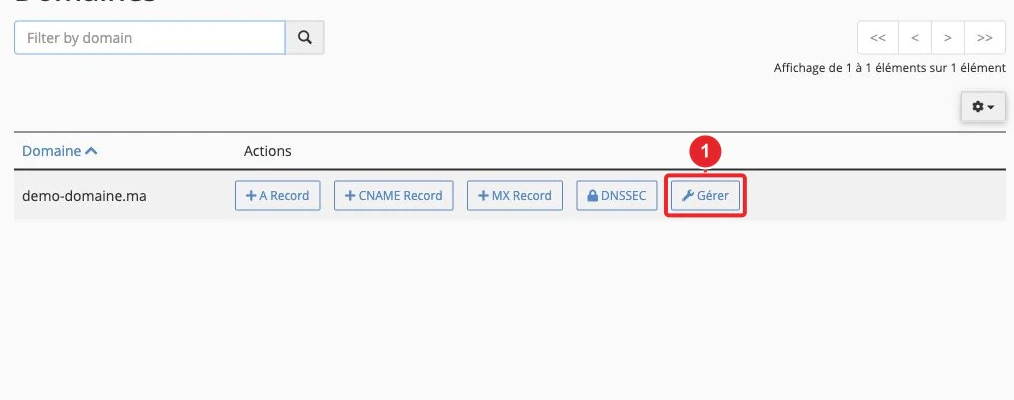
- Open Zone Editor then click Manage for the domain in question.
- Locate the column TTL in the list of records. To modify a record, click Edit/Modify, adjust the TTL value (in seconds) and save.
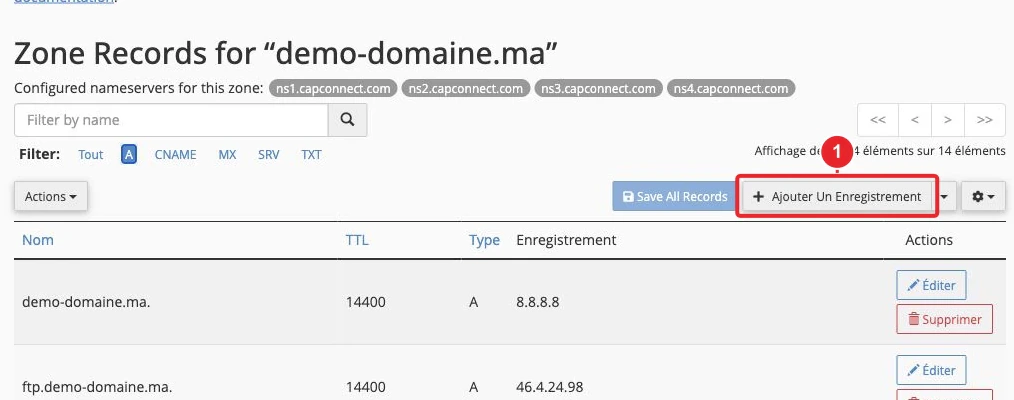
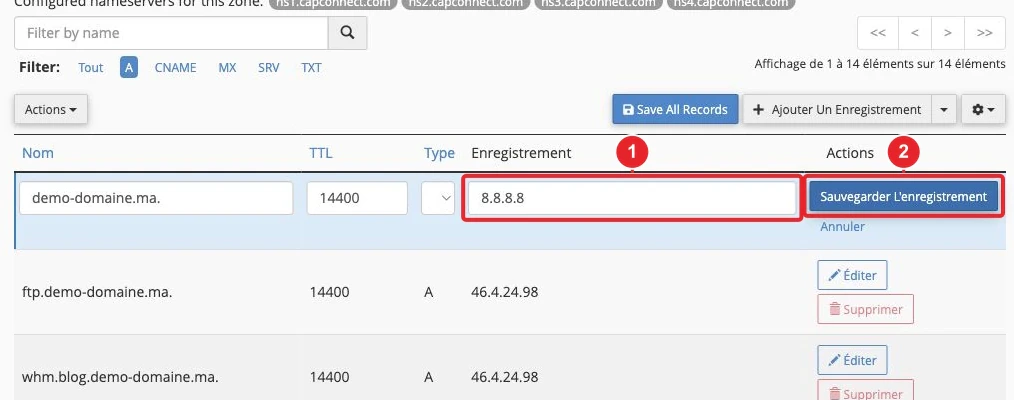
Practical tip: before a migration, lower the TTL (e.g. 600s) 24–48 hours beforehand to allow caches to expire more quickly. After migration and verification, raise the TTL (e.g. 3600s) to reduce DNS load.
Recommended procedure for a migration (e.g., IP change)
- 48–72 hours before: reduce the TTL to an acceptably low value (e.g. 600s) in the zone manager.
- Wait for the previous maximum TTL to elapse (the time required for existing caches to expire).
- Make the change (A/AAAA/CNAME/MX) on the authoritative server.
- Verify the authoritative server (dig @ns...), then check several public resolvers.
- When everything is stable, raise the TTL back to a standard value (3600s or more).
Troubleshooting: what to do if a change does not propagate?
- Be patient: some ISPs apply longer caches; wait 24–72 hours if necessary.
- Check NS delegation:
dig +short NS votredomaine.tld— the zone must be managed by the expected name servers. - Query the authoritative server: if it doesn't show the new value, the change wasn't published correctly.
- External zone / registrar confusion: if the domain's NS point to another provider (Cloudflare, registrar), make the changes with that provider — not in cPanel or the CAP CONNECT client area.
- Proxy services (Cloudflare, CDN): a proxy can present a different public IP. Disable the proxy if you want to see the real IP during tests.
- Flush local DNS and browser: flush DNS on your machine and clear the browser cache to avoid false positives.
- Windows:
ipconfig /flushdns - macOS:
sudo dscacheutil -flushcachethen, depending on the versionsudo killall -HUP mDNSResponder - Linux (systemd):
sudo systemd-resolve --flush-cachesor restartnscdif installed.
- Windows:
- If, after performing the checks below (dig +trace, querying the authoritative server) and waiting 48–72 hours, the situation has not changed, open a support ticket and attach the following:
- The affected domain name.
- The type of record modified (A, CNAME, MX, TXT, etc.) and the new value.
- Timestamp of the change (date/time UTC).
- Outputs of the commands
dig +short NS,dig @nsX votredomaine.tld TYPE +noall +answeranddig +trace votredomaine.tld.
Limitations and points to be aware of
- A very low TTL (e.g. 60s) greatly increases the number of queries to the authoritative server — avoid leaving it set permanently.
- Some registries impose values or behaviors at the TLD level (e.g. root zone refreshes). This can delay NS propagation.
- ISPs may ignore the TTL and keep a longer cache (sometimes 48–72 hours or more).
- DNSSEC: if the zone is signed, verify that the signatures remain valid after modification.
- A CNAME at the apex (root) is not permitted by the RFC — use ALIAS/ANAME if your provider offers it.
Useful commands and examples (summary)
- View the NS servers:
dig +short NS votredomaine.tld - Query an authoritative server:
dig @ns1.capconnect.com votredomaine.tld A +noall +answer - Check using Google DNS:
dig @8.8.8.8 votredomaine.tld A +short - Trace the resolution:
dig +trace votredomaine.tld - nslookup (Windows):
nslookup -type=MX votredomaine.tld 8.8.8.8
Useful internal links
- How do I change the DNS servers for my domain name? — if the NS delegation needs to be updated.
- DNS configuration for the Email PRO service — examples of MX/TXT records required for email.
- How do I access my cPanel account? — access the Zone Editor from cPanel.
Resources
In summary
To check propagation: first check the authoritative server, then query several public resolvers. The TTL explains why you sometimes see the old value — you must allow caches time to expire. Before a planned migration, lower the TTL in advance, perform the switchover, and raise the TTL after stabilization.
If you need help, prepare the outputs of the commands shown and open a support ticket attaching these items — this speeds up diagnosis.
Documentation consulted on October 16, 2026. Tools may vary depending on your hosting.